Should you enable VLAN awareness on a Proxmox Linux bridge?
Enable VLAN awareness on a Proxmox Linux bridge: one vmbr0, host on native VLAN 40 by DHCP, VMs tagged 10 and 30, plus switch and verify checks.
Overview
Yes, enabling VLAN awareness on a Proxmox Linux bridge is generally the recommended approach. The configuration stays cleaner, scales better, and you avoid creating one bridge per VLAN.
Without VLAN awareness, you typically create a separate bridge for each VLAN. That works, especially in small setups, but it gets messy as the number of VLANs grows, and on larger hosts or clusters dozens of bridges can clutter the configuration. A VLAN-aware bridge lets you define the allowed VLANs once and then assign tags directly in each VM’s network device settings.
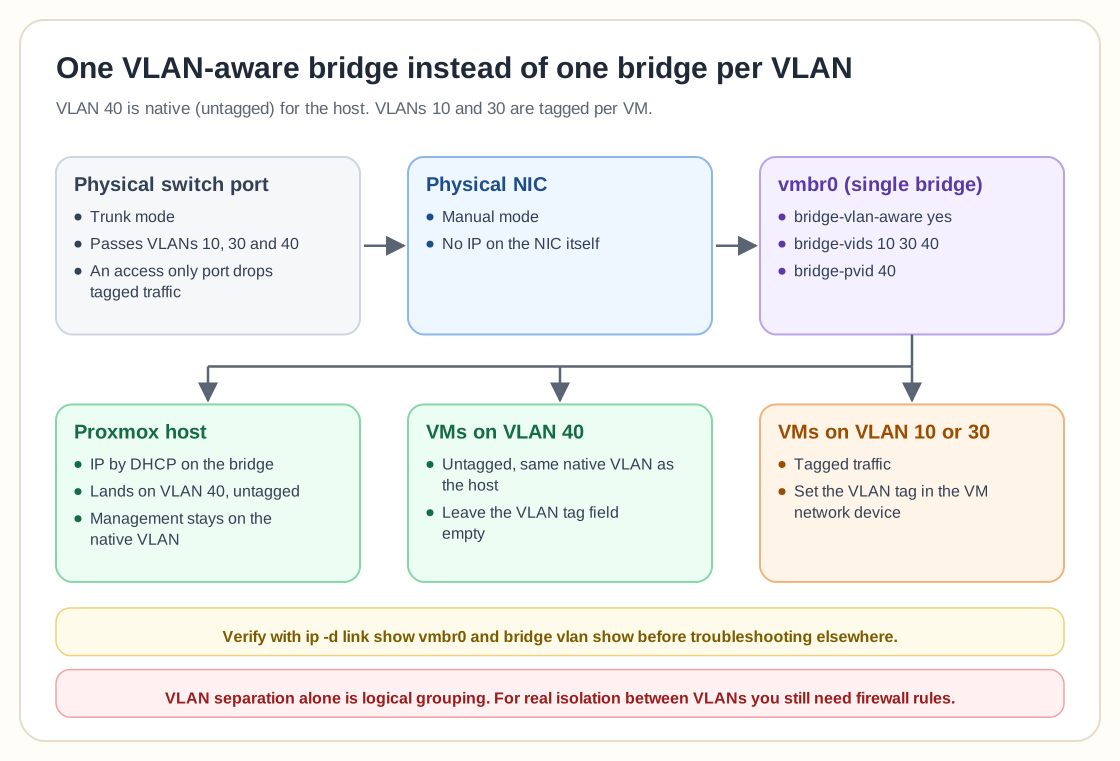
For your scenario, where VLAN 40 is native (untagged) and VLANs 10 and 30 are tagged, a typical configuration looks like this:
- Physical NIC in manual mode - Single bridge (vmbr0) - `bridge-vlan-aware yes` - `bridge-vids 10 30 40` - `bridge-pvid 40` - Host interface set to DHCP on the bridge
With this setup:
• The Proxmox host gets its IP via DHCP on VLAN 40 (untagged).
• VMs on VLAN 40 leave the VLAN tag field empty.
• VMs on VLAN 10 or 30 specify the VLAN tag in their network settings.
Management traffic stays isolated on the native VLAN, you can still place VMs flexibly, and the design is easy to standardize across cluster nodes.
You can also assign the host IP on a VLAN subinterface instead of the bridge, which keeps hypervisor traffic logically separate from VM switching. In larger multi-node environments, Proxmox SDN can abstract VLAN handling further.
Check two things once the bridge is configured. First, confirm your physical switch port is set to trunk mode and passes the same VLAN IDs you've defined in `bridge-vids`. A common source of "it's not working" reports is a switch port still configured as access-only, which silently drops tagged traffic before it ever reaches Proxmox. Second, if you also use the Proxmox firewall, remember that firewall rules are evaluated per VM network interface regardless of VLAN tag. If you need real network isolation between VLANs rather than logical grouping, you still need firewall rules; VLAN separation alone won't give you that.
To verify the configuration after applying it, `ip -d link show vmbr0` shows the bridge's VLAN filtering status, and `bridge vlan show` lists exactly which VLAN IDs are permitted on each interface. Both are useful for confirming your `bridge-vids` and `bridge-pvid` settings took effect before you start troubleshooting connectivity elsewhere.
For clusters in particular, VLAN-aware bridges are easier to organize and scale than one bridge per VLAN.
Need help with Proxmox?
Use the form below to get in touch about migrations, troubleshooting, and Proxmox design work.